
 Tiếng Việt
 English
 中文
 Español
 हिन्दी
 Français
 Português
 Русский
 Deutsch
 日本語
 한국어
 Italiano
 Bahasa Indonesia
 ไทย
 বাংলা
 ລາວ
 မြန်မာ
 العربية
 فارسی
 اردو
 Українська
 Română
 Azərbaycan
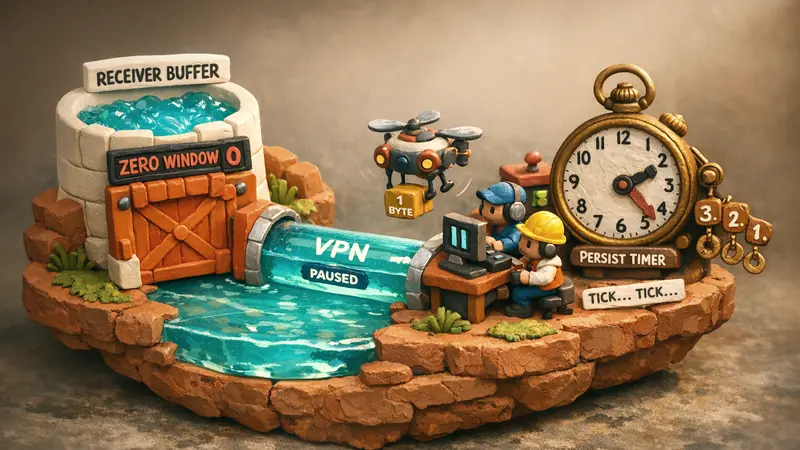
In high-throughput distributed environments and encrypted VPN tunnels, flow control ensures that a fast transmitter does not overwhelm a slow receiver. While congestion control (such as BBR or CUBIC) manages aggregate bandwidth across transit routers, TCP flow control operates end-to-end via the Receive Window (rcv_wnd) field inside the 20-byte TCP header. When a receiving host experiences internal CPU stalls, disk I/O bottlenecks, or socket buffer starvation, its kernel advertises a zero window (rcv_wnd = 0), signaling the sender to cease packet transmission immediately.
However, advertising a zero window introduces a critical failure mode: the silent deadlock. If the subsequent window update packet announcing available buffer capacity is dropped in transit, both endpoints hang indefinitely. To prevent permanent session stalls, TCP implements the Persist Timer and Zero Window Probes (ZWP), codified across RFC 793 and RFC 1122. In high-bandwidth VPN gateways handling tens of thousands of concurrent tunnels, managing zero window states is vital to prevent socket resource exhaustion and asymmetric Denial of Service attacks.
The Zero Window Deadlock and the Persist Timer
TCP acknowledgments that carry no payload are unreliable: the TCP protocol does not acknowledge pure ACK packets. This design decision avoids infinite recursion where an ACK of an ACK requires another ACK. Consequently, a race condition emerges whenever a receiver attempts to resume a paused data stream.
Sender (Client)                               Receiver (VPN Server)
      |                                                |
      | -------- Data Segment [Seq: 1000] -----------> | (Buffer full)
      | <------- ACK [Ack: 1000, Win: 0] ------------- | (Zero Window advertised)
      | [Transmission Suspended]                      |
      |                                                | (Application reads data)
      | < - - - - [ACK: 1000, Win: 65535] (LOST) - - - | (Window update dropped)
      |                                                |
      v [Deadlock: Waiting for Window Update]          v [Deadlock: Waiting for Data]
If the window update packet is dropped due to packet loss, physical jitter, or overlay encapsulation errors, the sender remains paused, waiting for an ACK with a non-zero window. Simultaneously, the receiver assumes the sender knows about the restored capacity and idles indefinitely.
To break this deadlock, TCP initializes a Persist Timer as soon as a zero-window acknowledgment is processed. In the Linux kernel, this timer is managed within net/ipv4/tcp_timer.c under the timer flag ICSK_TIME_PROBE0.
When the persist timer expires, the sender transmits a Zero Window Probe (ZWP). RFC 1122 Section 4.2.2.17 specifies that a probe segment contains either zero bytes or a single byte of payload, addressing sequence number snd_una - 1 or snd_nxt. Because the receiver receives an in-sequence or previously acknowledged byte, it is required by specification to reply with an immediate acknowledgment containing its current rcv_wnd.
Exponential Backoff and Kernel Mechanics
The persist timer employs an exponential backoff schedule comparable to the Retransmission Timeout (RTO). The initial interval matches the smoothed round-trip time calculation, bounded between TCP_RTO_MIN (typically 200 milliseconds) and TCP_RTO_MAX (120 seconds in Linux):
- Initial Probe Interval: Computed as
min(max(RTO, TCP_RTO_MIN), TCP_RTO_MAX). - Backoff Factor: Each subsequent probe doubles the wait time until reaching the 120-second ceiling.
- Probe Persistence: Unlike data retransmission timers that drop a connection after
tcp_retries2failures, standard TCP persist timers probe indefinitely as long as the remote endpoint acknowledges each probe with an explicitWin: 0.
This distinction is crucial for VPN administrators. A misbehaving or stalled client can hold open server-side socket memory indefinitely simply by continuing to respond to 1-byte probes with zero-window ACKs.
Silly Window Syndrome (SWS): Clark's Avoidance Heuristic
A related vulnerability in window management is Silly Window Syndrome (RFC 813). SWS occurs when either the sender transmits data in tiny fragments or the receiver advertises minuscule window expansions as soon as single bytes are drained from the receive buffer.
Consider a receiver socket whose buffer is drained 1 byte at a time by a slow application. If the TCP stack immediately advertises Win: 1, the sender transmits a 1-byte payload. Enclosing a 1-byte payload inside a 20-byte IPv4 header and a 20-byte TCP header yields a 41-byte packet. The protocol overhead reaches 97.5%, congesting transit links and overwhelming VPN crypto accelerators.
To eliminate SWS, David Clark established complementary avoidance heuristics codified in RFC 813 and RFC 1122:
| Component | Standard Behavior (Clark Avoidance) | Trigger Threshold |
|---|---|---|
| Receiver SWS | Suppress window updates until significant space opens | min(MSS, Buffer_Space / 2) |
| Sender SWS | Delay transmission of partial segments | Full MSS or Receiver Win >= MSS / 2 |
| Persist Fallback | Transmit single-byte probe if persist timer elapses | Timer expiration under Win: 0 |
In Linux, the receiver calculates tcp_select_initial_window() and suppresses incremental advertisements until at least one Maximum Segment Size (MSS) or half of the total receive buffer space (sk_rcvbuf / 2) is reclaimed.
Linux Kernel Tuning: Window Clamping and Socket Buffer Protection
In large VPN concentrators hosting thousands of tunnels, unchecked zero-window states expose systems to resource exhaustion. The notorious "Sockstress" vulnerability demonstrated that an adversary could open tens of thousands of TCP connections, advertise a zero window, and force the server kernel to commit megabytes of kernel memory to persist timers and socket buffers.
Linux provides several kernel parameters to regulate receive window advertising and memory consumption.
Restricting Advertised Windows with Window Clamping
The tcp_window_clamping socket option and related sysctl settings limit the maximum receive window advertised to peers:
# Set global TCP memory boundaries (min, default, max pages)
sudo sysctl -w net.ipv4.tcp_rmem="4096 87380 6291456"
sudo sysctl -w net.ipv4.tcp_wmem="4096 65536 4194304"

# Enforce proactive orphan socket cleanup under memory pressure
sudo sysctl -w net.ipv4.tcp_orphan_retries=2
sudo sysctl -w net.ipv4.tcp_max_orphans=32768
At the application level, high-density network servers use the TCP_WINDOW_CLAMP socket option via setsockopt(). This clamps the advertised receive window down to a bounded ceiling, preventing clients from inflating their window scale factors beyond gateway memory thresholds.
Mitigating Sockstress and Orphan Stalls
Because standard persist timers can run indefinitely when the client ACKs probes with Win: 0, VPN daemons implement user timeouts via TCP_USER_TIMEOUT (RFC 5482). When TCP_USER_TIMEOUT is configured, the kernel enforces a maximum threshold for unacknowledged data or unresolved zero-window states. If the remote peer remains in a zero-window condition longer than the specified threshold, the kernel terminates the socket, reclaiming transmission and receive buffers.
Architectural Integration in RiceGuard and Core L3 VPN Overlays
Flow control becomes multifaceted when client traffic is encapsulated within encrypted UDP overlays. If the inner TCP stream stalls due to a zero window, transmitting unthrottled outer UDP tunnel packets wastes transit bandwidth and CPU cycles on unnecessary cryptographic operations.
Modern architectures decouple tunnel transport from application-level flow control:
- Inner Stream Monitoring: The RiceGuard data plane inspects inner TCP header window advertisements. When a tunnel client advertises a zero window, the gateway throttles the associated virtual queue, preventing buffer bloat across userspace ring buffers.
- Proactive Backpressure: The Core L3 VPN engine utilizes zero-copy packet rings. Rather than allowing an inner TCP socket to crash into hard buffer exhaustion, the stack applies window clamping early, signaling graceful throttling before packet drops occur.
- Persist Probe Synthesis: If an outer lossy connection drops a critical non-zero window update, the gateway's overlay controller synthesizes an immediate zero-window probe, re-synchronizing buffer state without waiting for full kernel backoff cycles.
Summary: Deterministic Flow Control in Modern Gateways
Understanding TCP Zero Window Probing and Silly Window Syndrome avoidance allows network architects to balance responsiveness against memory safety. Flow control is not merely a mechanism for slowing down senders; it is an active protocol state machine designed to prevent deadlocks and maintain transport integrity.
By combining David Clark's SWS avoidance algorithms with Linux window clamping and strict TCP_USER_TIMEOUT policies, network operators eliminate silent deadlocks and protect infrastructure against buffer exhaustion. Protect your network infrastructure and maintain low-jitter tunnel performance with Get VPNRice.


