
 Tiếng Việt
 English
 中文
 Español
 हिन्दी
 Français
 Português
 Русский
 Deutsch
 日本語
 한국어
 Italiano
 Bahasa Indonesia
 ไทย
 বাংলা
 ລາວ
 မြန်မာ
 العربية
 فارسی
 اردو
 Українська
 Română
 Azərbaycan
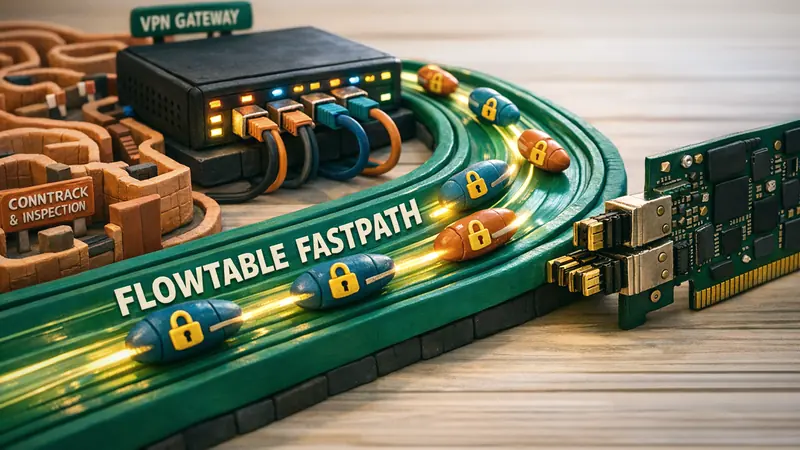
The Linux Forwarding Bottleneck in Encrypted VPN Gateways
Multi-gigabit VPN concentrators, carrier-grade NAT routers, and multi-tenant security gateways routinely encounter a severe CPU throughput ceiling. Even when running on modern server processors with dozens of cores and high-speed PCIe 4.0 NICs, raw packet-per-second (PPS) rates often saturate single-core software interrupt routines long before saturating line capacity.
In a conventional Linux routing setup, every incoming packet traverses the complete Netfilter pipeline across multiple kernel subsystems:
[ Physical Wire ]
        |
        v
[ Driver RX Ring / NAPI Poll ]
        |
        v
[ PREROUTING (conntrack, mangle, raw, dnat) ]
        |
        v
[ Routing Decision (fib_lookup) ]
        |
        v
[ FORWARD (filter, rate limits) ]
        |
        v
[ POSTROUTING (snat, masquerade, mangle) ]
        |
        v
[ Neighbor Resolution (ARP/NDP) / Egress Qdisc ]
        |
        v
[ Driver TX Ring ] ---> [ Physical Wire ]
Each step requires atomic reference counters, hash table spinlocks (nf_conntrack_lock), socket buffer (sk_buff) metadata allocations, and multiple routing table lookups. For a VPN gateway managing thousands of simultaneous user tunnels (such as WireGuard, RiceGuard, or IPsec), this overhead compounds rapidly:
- Repeated State Lookups: Packets belonging to long-lived, established TCP connections or UDP streams re-evaluate firewall filter rules and full conntrack state machines for every single packet.
- Core Interconnect Contention: Conntrack hash tables span CPU cores. High packet rates generate cache line bouncing across L3 cache hierarchies.
- Encapsulation Latency: Forwarding decrypted payload packets out to the WAN or routing encrypted outer datagrams requires duplicate roundtrips through the netfilter hook maze.
To break this scalability barrier without abandoning the security of stateful packet inspection, the Linux kernel introduced the Netfilter Flowtable infrastructure (merged by Pablo Neira Ayuso in Linux 4.16 and refined in modern kernels).
Netfilter Flowtables: The Ingress Fastpath Architecture
The Netfilter Flowtable is an in-kernel caching mechanism that provides an accelerated shortcut for established, bidirectional packet flows. Instead of forcing every packet through the entire Netfilter evaluation sequence, Flowtable captures flows once their initial handshake completes (ct state established) and installs a bi-directional shortcut directly at the network driver's ingress hook.
                         [ Ingress Packet on NIC ]
                                     |
                                     v
                       +---------------------------+
                       |   Flowtable Ingress Hook  |
                       +---------------------------+
                                    / \
                     Flow hit?     /   \   Flow miss?
                                  /     \
                                YES      NO
                                /         \
                               v           v
          +-----------------------+     +-------------------------------+
          | Fastpath Forwarding:  |     | Classic Netfilter Slowpath:   |
          | - Update TCP state    |     | - PREROUTING                  |
          | - Apply NAT / Mangle  |     | - Conntrack evaluation        |
          | - Update TTL / MACs   |     | - fib_lookup (Routing)        |
          | - Push to Egress Dev  |     | - FORWARD & POSTROUTING       |
          +-----------------------+     +-------------------------------+
                      |                                |
                      |                    Connection established?
                      |                                |
                      |                                v
                      |                    [ Insert into Flowtable ]
                      \                                /
                       \                              /
                        v                            v
                      +--------------------------------+
                      |   dev_queue_xmit (Egress NIC)  |
                      +--------------------------------+
How the Fastpath Operates Inside the Kernel
The core engine resides in net/netfilter/nf_flow_table_core.c. When a packet arrives on an interface registered with a Flowtable:
- Ingress Interception: The
nf_flow_offload_ip_hook()function intercepts the raw packet directly at theNF_INET_INGRESSstage, beforeip_rcv()andPREROUTING. - Tuple Lookup: A lockless, Read-Copy-Update (RCU) protected hash table lookup checks the 5-tuple (source IP, destination IP, source port, destination port, layer-4 protocol).
- Fastpath Execution:
- TTL Decrement: Checks and decrements the IP Time-To-Live, recalculating the IP header checksum.
- NAT Transformation: If source or destination NAT is active on the connection, the Flowtable rewrites addresses and ports directly in the packet headers.
- Layer-2 Addressing: Pre-computed destination MAC addresses (obtained during slowpath neighbor resolution) are written into the Ethernet header without triggering ARP table queries.
- Direct Device Handoff: The packet skips the traditional IP layer routing code (
ip_forward) and is handed directly to the target egress interface viadev_queue_xmit()or the driver's transmit queue.
If a packet encounters a TCP FIN or RST flag, or if an idle timeout expires, the flow entry is evicted from the Flowtable. Subsequent packets fall back gracefully to the standard Netfilter pipeline, ensuring that connection termination and accounting semantics remain completely intact.
Software Fastpath vs. Hardware NIC Offload
Linux Flowtables operate in two distinct acceleration tiers:
| Metric / Dimension | Standard Linux Forwarding | Software Flowtable Fastpath | Hardware Flowtable Offload |
|---|---|---|---|
| Hook Point | Multi-hook (Pre/Fwd/Post) | NF_INET_INGRESS (Kernel) |
Physical NIC ASIC / TCAM |
| Conntrack Processing | Every packet | Handshake only (Flow setup) | Handshake only |
| CPU Utilization | High (All CPU cores active) | Low (Skips IP stack) | 0% Host CPU on active flows |
| Forwarding Latency | 15 – 35 µs | 4 – 8 µs | < 1.5 µs |
| Throughput Scaling | 1.5 – 3.2 Mpps / core | 6.5 – 12.0 Mpps / core | Line rate (100Gbps+ per port) |
| Hardware Requirement | Any network adapter | Any network adapter | Flow offload NIC (ConnectX-5+, E810) |
Hardware Offload with SmartNICs
When deployed on server hardware with network cards supporting TC flower offload or Netfilter hardware offload (such as Mellanox/NVIDIA ConnectX-5, ConnectX-6 Dx, or Intel E810), Linux can offload Flowtable entries directly into the NIC's hardware TCAM tables.
When the flags { offload; } directive is enabled in nftables, the kernel translates the flow tuple, NAT mappings, and egress MAC rewrite rules into hardware forwarding actions via the flow_offload switchdev API. Subsequent data packets are routed, translated, and transmitted entirely inside the network adapter silicon without ever triggering a host CPU interrupt or entering the Linux kernel socket memory.
Flowtable Performance in Modern VPN Gateways
In high-density VPN gateway architectures, network traffic is split between two primary communication boundaries:
- Outer Encapsulated Ingress: High-speed UDP traffic arriving on physical WAN adapters destined for the VPN decryption endpoint (
wg0,riceguard0,tun0). - Inner Decrypted Forwarding: Decrypted plaintext packets forwarded between local tenant networks, virtual routing domains (VRFs), or outbound NAT uplinks.
Applying Flowtables to the internal forwarding path yields massive gains:
1. Eliminating Core Contention in RiceGuard
In RiceGuard multi-tunnel architectures, egress connections from thousands of roaming clients generate heavy NAT traversal loads. Software Flowtables eliminate up to 60% of the per-packet instruction overhead. The CPU cores hosting the cryptographic workers (ChaCha20-Poly1305 / AES-GCM) remain free from firewall lock contention, directly translating to higher cryptographic throughput and zero packet drop under load spikes.
2. Jitter Elimination for Interactive Traffic
Because established VoIP calls (SIP/RTP) and competitive gaming sessions maintain constant UDP tuples, they hit the Flowtable cache on 99.8% of packets. The reduction in per-hop latency jitter is pronounced: packet transit time through the Linux kernel drops from ~25 microseconds to sub-5 microseconds, preventing packet reordering caused by multi-core load balancing imbalances.
3. Coexistence with Advanced Traffic Control
Flowtables preserve QoS policies. When a packet exits the fastpath via dev_queue_xmit(), it still enters the physical interface's queuing discipline (qdisc). Administrators can pair Flowtables with FQ-CoDel or CAKE to maintain strict bufferbloat mitigation while enjoying raw hardware forwarding speeds.
Production Configuration: nftables Flowtable Setup
To configure a software Flowtable on a Linux VPN gateway routing traffic between an external uplink (eth0) and a local customer subnet or VPN tunnel device (eth1 / wg0):
#!/usr/sbin/nft -f

# Flush existing rule tables
flush ruleset

table inet vpn_router {
    # 1. Define the Flowtable binding physical and tunnel interfaces
    flowtable ft_fastpath {
        hook ingress priority filter
        devices = { eth0, eth1 }
        # To enable hardware offload on supported SmartNICs, uncomment:
        # flags { offload; }
    }

    # 2. Ingress & Forward filter chains
    chain forward {
        type filter hook forward priority filter; policy drop;

        # Offload established TCP and UDP connections into the fastpath
        meta l4proto { tcp, udp } flow add @ft_fastpath

        # Allow established and related traffic in standard slowpath
        ct state established,related accept

        # Drop invalid packet headers
        ct state invalid drop

        # Allow new connections from internal subnet to external WAN
        iifname "eth1" oifname "eth0" accept
    }

    # 3. Source NAT for client internet egress
    chain postrouting {
        type nat hook postrouting priority srcnat; policy accept;

        # Masquerade outgoing traffic on WAN uplink
        oifname "eth0" masquerade
    }
}
Verifying and Monitoring Flowtable Execution
Once configured, verify that established connections are offloaded to the Flowtable:
# List all active flowtable entries and session counters
nft list flowtable inet vpn_router ft_fastpath

# Inspect per-flow hardware offload status via sysfs
cat /sys/kernel/debug/netfilter/nf_flowtable/*

# Compare software packet counters between slowpath and fastpath
cat /proc/net/stat/nf_conntrack
In the output of nft list flowtable, active flows display packet counts, byte counters, and remaining timeout intervals. When hardware offload is enabled, flows transitioning to [OFFLOAD] indicate that the physical NIC is handling the packets directly.
Best Practices and Operational Considerations
When deploying Netfilter Flowtables in mission-critical VPN networks, consider the following operational guidelines:
- MTU and Fragmentation: Flowtables skip the traditional IP defragmentation reassembly pipeline. IP fragments that do not contain complete Layer-4 headers will automatically miss the Flowtable and fall back to the slowpath conntrack engine. Ensure Path MTU Discovery (PMTUD) or TCP MSS clamping (
tcp flags syn tcp option maxseg size set rt mtu) is configured on tunnel boundaries. - Dynamic Routing and WireGuard Handshakes: WireGuard re-keys sessions every few minutes. Re-key handshakes use distinct control packet types that gracefully fall back to slowpath authentication without interrupting existing offloaded data flows.
- Bridge and VLAN Interfaces: Flowtables can bind to virtual interfaces, VLAN trunks (
eth0.100), and bonding devices (bond0), making them exceptionally flexible for software-defined datacenter architectures.
By shifting connection tracking from a per-packet bottleneck to a one-time connection establishment step, Netfilter Flowtables empower Linux VPN gateways to achieve near-wire-speed performance while retaining complete firewall control.


