Tiếng Việt
 English
 中文
 Español
 हिन्दी
 Français
 Português
 Русский
 Deutsch
 日本語
 한국어
 Italiano
 Bahasa Indonesia
 ไทย
 বাংলা
 ລາວ
 မြန်မာ
 العربية
 فارسی
 اردو
 Українська
 Română
 Azərbaycan
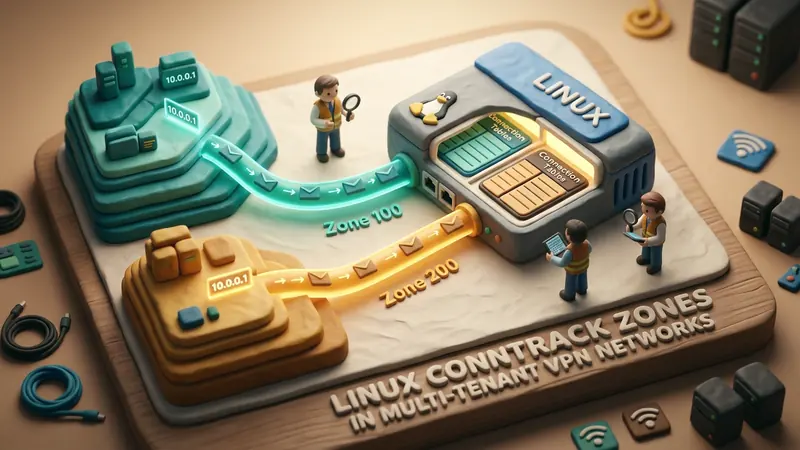
Multi-tenant VPN gateways operating at enterprise scale face a fundamental architectural hurdle: address space overlap. When aggregating tunnels across disparate organizations, branch offices, and client environments, network architects invariably encounter identical private IPv4 subnets defined by RFC 1918. Two separate corporate clients frequently assign 10.0.0.0/24 or 192.168.1.0/24 to their internal workloads.
When these distinct tunnels terminate on a single shared Linux security gateway, standard stateful firewall inspection collapses. The Linux Netfilter connection tracking subsystem (nf_conntrack) tracks sessions using a 5-tuple: source IP, destination IP, source port, destination port, and protocol. If Host A in Tenant 1 (10.0.0.5:52140) and Host B in Tenant 2 (10.0.0.5:52140) initiate concurrent TCP handshakes toward the same public service (1.1.1.1:443), Netfilter encounters identical hash keys. Without isolation, the kernel misinterprets Tenant 2's packets as belonging to Tenant 1's active session, corrupting TCP sequence numbers, inducing state resets, and creating cross-tenant data leakage vulnerabilities.
Linux connection tracking zones (ct zone) resolve this collision cleanly within the kernel data path. By incorporating a 16-bit zone identifier into the tracking key, the kernel partitions its global session table into isolated logical namespaces without the operational overhead of spinning up separate network namespaces.
Multi-Tenant Packet Collision vs. Zone Isolation:

Without CT Zones (Collision Risk):
Tenant 1: [10.0.0.5:52140 -> 1.1.1.1:443] ──┐
                                             ├──> Tuple Hash Collision ──> Session Desync / Drop
Tenant 2: [10.0.0.5:52140 -> 1.1.1.1:443] ──┘

With Netfilter CT Zones:
Tenant 1: [10.0.0.5:52140 -> 1.1.1.1:443] + Zone 100 ──> Bucket A [State: ESTABLISHED]
Tenant 2: [10.0.0.5:52140 -> 1.1.1.1:443] + Zone 200 ──> Bucket B [State: ESTABLISHED]
The Anatomy of Netfilter Tuple Collisions
To understand why traditional state tracking fails with overlapping subnets, consider the internal mechanics of net/netfilter/nf_conntrack_core.c. As ingress frames traverse the PREROUTING hook, Netfilter extracts packet metadata into a canonical structure:
struct nf_conntrack_tuple {
    struct nf_conntrack_man src;
    struct {
        union nf_inet_addr u3;
        union {
            __be16 all;
            struct { __be16 port; } tcp;
            struct { __be16 port; } udp;
        } u;
        u_int8_t protonum;
        u_int8_t dir;
    } dst;
};
The kernel computes a hash over this tuple using Jenkins hash or SipHash functions to index a global hash table (nf_conntrack_hash). When a matching entry exists, resolve_normal_ct() attaches the session reference (struct nf_conn) to the sk_buff.
When two distinct client tunnels share identical private IP spaces, this lookup becomes ambiguous. If Tenant 1 and Tenant 2 generate packets with identical 5-tuples:
__nf_conntrack_find_get()returns Tenant 1's existing session entry for Tenant 2's fresh packet.- The TCP state tracker in
nf_conntrack_proto_tcp.ccompares sequence numbers. Because Tenant 2's independent TCP stack generated a completely unrelated initial sequence number (ISN), the packet falls outside the expected TCP window. - Netfilter flags the frame as
TCP_CONNTRACK_SYN_SENTorINVALID, frequently emitting an out-of-bandTCP RSTthat severs the connection. - Source Network Address Translation (SNAT) routines allocate egress ports against the colliding entry, mixing up packet headers during reverse translation.
Network namespaces (ip netns) offer complete network stack virtualization to separate these tables. However, assigning a dedicated network namespace to every VPN client introduces severe penalties: virtual Ethernet (veth) pair latency, multiple routing cache layers, increased memory consumption, and extreme complexity when managing shared security policies, Anycast routing, and unified intrusion detection.
In-Kernel Zone Partitioning: struct nf_conntrack_zone
Connection tracking zones eliminate this tradeoff by decoupling connection tracking isolation from network namespace virtualization. A zone is an integer identifier ranging from 0 to 65535 attached to the packet tracking context.
In include/net/netfilter/nf_conntrack_zones.h, the kernel defines the zone structure:
struct nf_conntrack_zone {
    u16 id;
    u8 flags;
    u8 dir;
};

#define NF_CT_DEFAULT_ZONE_ID   0
#define NF_CT_ZONE_DIR_ORIG     (1 << 0)
#define NF_CT_ZONE_DIR_REPL     (1 << 1)
When zones are enabled, Netfilter extends the hash calculation. Instead of hashing strictly the 5-tuple, the hash function incorporates the 16-bit zone->id:
$$\text{Hash Key} = \text{hash_tuple}(\text{tuple}) \oplus \text{hash_zone}(\text{zone_id})$$
Because the zone identifier is embedded directly into struct nf_conntrack_tuple_hash, two identical 5-tuples belonging to Zone 100 and Zone 200 hash to separate entries within nf_conntrack_hash. Both sessions coexist simultaneously in memory without lock contention or cross-tenant inspection interference.
Netfilter Hash Table Architecture with Zones:

nf_conntrack_hash Table
├── Bucket 0x3A4B: [Tuple: 10.0.0.5:52140 -> 1.1.1.1:443 | Zone: 100] (Tenant 1)
├── Bucket 0x8F12: [Tuple: 10.0.0.5:52140 -> 1.1.1.1:443 | Zone: 200] (Tenant 2)
└── Bucket 0xC201: [Tuple: 192.168.1.15:49152 -> 8.8.8.8:53 | Zone: 0]   (Default)
The flags field also enables directional zone binding. Using NF_CT_ZONE_DIR_ORIG and NF_CT_ZONE_DIR_REPL, administrators can assign packets entering from an untrusted client tunnel to Zone 100 on the forward path, while routing replies through an inspection gateway in Zone 0, establishing clean demarcation boundaries.
Configuring Conntrack Zones with Modern nftables
Deploying connection tracking zones requires setting the zone identifier early in the packet processing pipeline—specifically inside the raw priority hook of the prerouting chain, before standard Netfilter connection tracking hooks execute.
The modern nftables syntax handles zone assignment cleanly based on input interfaces, VRF domains, or packet marks. Consider a gateway aggregating two WireGuard or IPsec tunnels (wg-tenant1 and wg-tenant2) with overlapping address spaces:
table inet vpn_firewall {
    chain raw_prerouting {
        type filter hook prerouting priority raw; policy accept;

        # Assign isolated conntrack zones based on ingress interface
        iifname "wg-tenant1" ct zone set 100
        iifname "wg-tenant2" ct zone set 200
    }

    chain forward {
        type filter hook forward priority filter; policy drop;

        # Permit established state independently per zone
        ct state established,related accept

        # Policy enforcement for Tenant 1 (Zone 100)
        ct zone 100 oifname "eth0" accept

        # Policy enforcement for Tenant 2 (Zone 200)
        ct zone 200 oifname "eth0" accept
    }

    chain postrouting {
        type nat hook postrouting priority srcnat; policy accept;

        # Independent masquerade translations per tenant zone
        ct zone 100 oifname "eth0" masquerade
        ct zone 200 oifname "eth0" masquerade
    }
}
In this configuration, Netfilter segregates state tracking before evaluating firewall policies. When Tenant 1 and Tenant 2 initiate outbound traffic, masquerade allocates ephemeral public ports from the gateway's public interface (eth0). Because NAT tracking is zone-aware, the kernel tracks port allocations independently within each zone, ensuring that return packets arriving on eth0 are accurately demultiplexed and forwarded back to the correct tenant tunnel.
To inspect active tracked sessions and verify zone separation on a live Linux system, administrators use conntrack:
# Query connections isolated to Tenant 1
conntrack -L -z 100

# Query connections isolated to Tenant 2
conntrack -L -z 200
The output confirms that identical IP pairs are tracked with independent state counters and timeout windows:
tcp 6 431999 ESTABLISHED src=10.0.0.5 dst=1.1.1.1 sport=52140 dport=443 [OFFLOAD] zone: 100
tcp 6 431999 ESTABLISHED src=10.0.0.5 dst=1.1.1.1 sport=52140 dport=443 [OFFLOAD] zone: 200
Performance Scaling and Memory Overhead
A common concern among network engineers is whether connection tracking zones degrade packet forwarding throughput under high load. Extensive benchmarking demonstrates that zone lookups impose zero measurable overhead compared to flat conntrack tables.
Because the zone integer is included directly in the 64-bit hashing key, calculating the hash bucket incurs no additional pointer dereferences or memory lookups. The session comparison loop in nf_conntrack_tuple_equal() evaluates zone->id alongside IP addresses in a single SIMD-optimized or register-level comparison.
Forwarding Throughput vs. Isolation Mechanism:
────────────────────────────────────────────────────────────────
Isolation Architecture      Forwarding Rate    Memory per Tenant
────────────────────────────────────────────────────────────────
Network Namespaces (netns)   1.85 Mpps          ~4.2 MB (base)
Conntrack Zones (ct zone)   3.42 Mpps          0 MB (shared pool)
Raw Stateless Routing       3.55 Mpps          0 MB (no state)
────────────────────────────────────────────────────────────────
To optimize high-density gateways handling hundreds of thousands of concurrent connections across hundreds of zones, tuning system buffer allocation is essential:
# Expand hash table buckets to minimize bucket chain collisions
echo 262144 > /sys/module/nf_conntrack/parameters/hashsize

# Increase maximum concurrent tracked connections
sysctl -w net.netfilter.nf_conntrack_max = 1048576

# Accelerate inactive TCP state reclamation
sysctl -w net.netfilter.nf_conntrack_tcp_timeout_established = 86400
sysctl -w net.netfilter.nf_conntrack_tcp_timeout_close_wait = 60
By expanding hashsize to match expected peak concurrent connections, hash bucket depth remains under two entries per bucket, preserving $O(1)$ lookup latency even when serving hundreds of enterprise tenants with overlapping internal subnets.
Secure Architectural Design in Enterprise VPNs
In modern multi-tenant infrastructures, connection tracking zones serve as the foundational building block for zero-leak traffic routing. When combined with Linux Virtual Routing and Forwarding (VRF) or policy routing tables (ip rule), ct zones provide complete isolation across layers 3 and 4:
- Ingress Demultiplexing: Tunnel endpoints attach incoming packets to a VRF device or interface-specific conntrack zone.
- Policy Enforcement: Security rules isolate tenant zones, blocking inter-zone forwarding unless explicit cross-tenant peering rules are provisioned.
- Stateful NAT Mapping: Kernel NAT routines translate colliding private addresses into unique external port ranges without state desynchronization.
VPNRice integrates these kernel-level primitives directly into its RiceGuard infrastructure. By orchestrating hardware-accelerated connection tracking zones, cryptographic tunnel isolation, and automated DNS leak mitigation, RiceGuard delivers multi-tenant enterprise connectivity that eliminates cross-tenant route collisions while maintaining line-rate packet throughput.
Network engineers managing multi-tenant VPN infrastructure should embrace connection tracking zones as a standard design pattern. Instead of accepting the latency penalties and administrative complexity of sprawling network namespace architectures, deploying ct zone primitives inside modern nftables rulesets provides robust, mathematically isolated, and wire-speed stateful security across overlapping enterprise networks.