Tiếng Việt
 English
 中文
 Español
 हिन्दी
 Français
 Português
 Русский
 Deutsch
 日本語
 한국어
 Italiano
 Bahasa Indonesia
 ไทย
 বাংলা
 ລາວ
 မြန်မာ
 العربية
 فارسی
 اردو
 Українська
 Română
 Azərbaycan
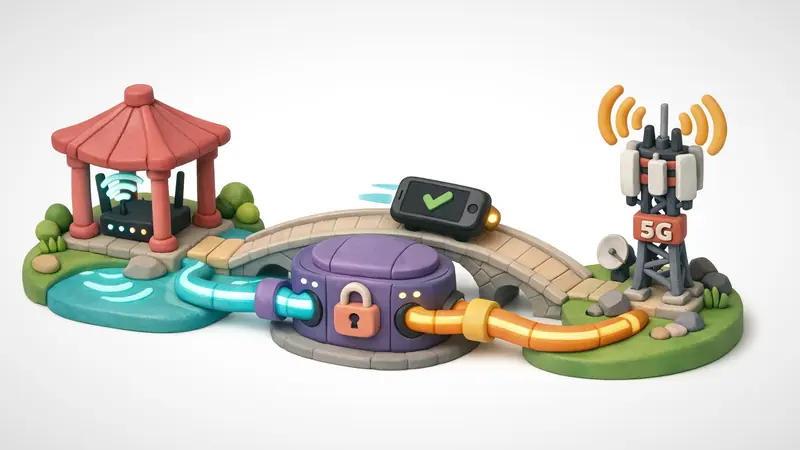
Mobile network connectivity is inherently unstable. When a user carrying a connected device steps out of their home or office, the local Wi-Fi radio signal rapidly attenuates, forcing the operating system to negotiate a handover to a cellular 4G LTE or 5G radio interface. In classical transport architectures, this physical migration shifts the device's public IP address and external port allocation. For traditional virtual private network architectures, such physical network transitions trigger connection stalls, packet drops, and disruptive renegotiation delays.
WireGuard revolutionizes this paradigm through its dynamic endpoint roaming mechanism. Built directly on top of Cryptokey Routing and state-minimized kernel networking, WireGuard decouples cryptographic identity from network transport addresses. By examining how WireGuard processes incoming cryptographically authenticated packets, network architects can understand why tunnels remain stable across cellular towers and Wi-Fi networks without dropping active voice sessions or encrypted data streams.
The Brittleness of Legacy VPN Tunnels During Physical Roaming
Legacy tunneling protocols—most notably OpenVPN over TCP or UDP and classical IPsec ESP—were designed during an era dominated by stationary desktop computers with static network attachments. Consequently, their protocol state machines tie the cryptographic security association (SA) directly to a fixed socket tuple comprising source IP, destination IP, source port, and destination port.
[Traditional VPN Handover Failure]
Mobile Client (Home Wi-Fi: 192.168.1.10 -> Public: 203.0.113.10:41234)
   | === Established Tunnel Session ===> VPN Gateway (198.51.100.1:1194)
[User walks to street -> Wi-Fi disconnects -> Cell tower attaches]
Mobile Client (Cellular 5G CGNAT -> Public: 198.51.100.50:58210)
   | --- Encrypted Packets Transmitted ---> VPN Gateway (Expects 203.0.113.10)
   X [GATEWAY DROPS PACKET: Source address mismatch or state desynchronization]
   X [Session timeout -> Full re-handshake required (2-5 seconds freeze)]
When a mobile device transitions across network boundaries:
- The cellular modem receives a completely different carrier-grade NAT (CGNAT) public IPv4 or IPv6 address.
- The remote VPN gateway continues transmitting response traffic to the old Wi-Fi socket tuple, where packets are silently discarded by intermediate routing nodes.
- In IPsec, resolving this mismatch requires the IKEv2 Mobility and Multihoming Protocol (MOBIKE, RFC 4555). MOBIKE introduces complicated control signaling, cookie validations, and multiple round-trip time (RTT) verification exchanges before updating security associations.
- In OpenVPN, clients must wait for dead peer detection (DPD) timers to expire, tear down the transport connection, and execute an expensive TLS handshake from scratch, causing noticeable service interruptions.
Cryptokey Routing and the Stateless Endpoint Update Mechanism
WireGuard eliminates the concept of an ephemeral connection state machine. Instead, it introduces Cryptokey Routing: a system where public cryptographic keys are mapped directly to allowable IP address prefixes inside the tunnel (AllowedIPs), while the external physical endpoint is treated as an opportunistic, dynamically updated cache entry.
Every WireGuard peer configuration maintains an internal endpoint structure:
struct wireguard_peer {
    u8 public_key[32];
    struct noise_symmetric_key current_key;
    struct allowedips_node allowed_ips;
    struct endpoint {
        union {
            struct sockaddr_in in;
            struct sockaddr_in6 in6;
        } addr;
    } endpoint;
};
Rather than requiring an explicit control message or a renegotiation handshake, WireGuard updates this endpoint.addr opportunistically. Whenever the server receives a valid data packet that passes ChaCha20-Poly1305 authentication, it inspects the UDP header of the incoming datagram. If the source IP address or UDP port differs from the cached endpoint, the server immediately updates its internal table to point to the new socket address. Subsequent outbound packets destined for that peer are instantly routed to the updated destination.
Kernel Execution Flow: From Packet Arrival to Socket Rebinding
To understand how roaming occurs in microsecond intervals, examine the execution path inside the Linux kernel implementation (drivers/net/wireguard/receive.c).
[Incoming Encrypted Datagram on UDP Port 51820]
                       |
                       v
         [Lookup Peer by Receiver Index]
                       |
                       v
     [Validate AEAD: ChaCha20-Poly1305 MAC]
          /                         \
     (Invalid)                    (Valid)
        /                             \
       v                               v
[Drop Immediately]           [Check Anti-Replay Counter Window]
                                    /              \
                              (Duplicate)       (Fresh)
                                  /                 \
                                 v                   v
                          [Drop Packet]     [Update Peer Endpoint]
                                                     |
                                                     v
                                            [peer->endpoint = src]
                                                     |
                                                     v
                                          [Route Packet into wg0]
When an authenticated packet arrives at the host interface:
- Index Lookup: The kernel extracts the 32-bit
receiver_indexfrom the WireGuard header to locate the matching peer and session key in an O(1) hash table. - Cryptographic Authentication: The payload is decrypted using ChaCha20-Poly1305. If the 128-bit Poly1305 message authentication code (MAC) fails, the packet is discarded without modifying any system state.
- Anti-Replay Verification: The 64-bit packet counter is verified against a sliding bitmap window to prevent replay injection.
- Atomic Socket Rebinding: Having cryptographically proven the authenticity of the sender, the kernel invokes
wg_socket_set_peer_endpoint(). This updates the peer's destination endpoint to match the packet's source address.
Because these operations occur in kernel space during normal datagram processing, endpoint updates require zero supplementary network overhead and zero round trips.
Anti-Spoofing Guarantees and Return Routability Security
A common concern among network security engineers is whether opportunistic endpoint updates expose the VPN gateway to traffic diversion or denial-of-service (DoS) attacks. For example, could an attacker on a coffee shop network send forged UDP packets with a victim's IP address to divert tunnel traffic?
WireGuard's architecture guarantees robust anti-spoofing protection through its cryptographic ordering:
| Security Property | Implementation Mechanism | Defense Impact |
|---|---|---|
| Authentication Precedence | ChaCha20-Poly1305 validated before endpoint rewrite | Forged packets dropped before touching endpoint state |
| Counter Freshness | 64-bit sliding window anti-replay filter | Replayed packets from old networks cannot divert endpoints |
| Key Uniqueness | Curve25519 DH combined with ephemeral Noise keys | Only legitimate key holder can produce authentic MAC tags |
| Traffic Directionality | AllowedIPs table enforcement on decrypted IP headers | Prevents IP address spoofing from inside the tunnel |
Because the Poly1305 MAC authentication tag cannot be forged without possession of the ephemeral symmetric session key (providing 128 bits of cryptographic security), an off-path or on-path attacker cannot craft a packet that triggers an endpoint reassignment. Replaying previously captured packets also fails because replaying previously captured packets WireGuard's anti-replay counter rejects stale counter values.
NAT Traversal and Persistent Keepalive Dynamics in Mobile Networks
Mobile cellular carriers enforce strict NAT state timeouts on intermediate middleboxes to conserve carrier-grade IPv4 pool allocations. Often, a CGNAT UDP binding expires after as little as 30 to 60 seconds of inactivity.
WireGuard resolves bidirectional reachability across dynamic middleboxes using two symbiotic mechanisms:
- Dynamic Re-punching: Whenever a mobile client sends outbound traffic, the outward UDP datagram punches a fresh hole through the carrier's NAT gateway, updating the server's endpoint cache in the process.
- Persistent Keepalive: For scenarios where the mobile client must receive unsolicited incoming connections (such as VoIP calls or remote SSH sessions), WireGuard provides the
PersistentKeepaliveconfiguration directive. When set (for example,PersistentKeepalive = 25), WireGuard automatically transmits a silent, 32-byte authenticated zero-payload packet every 25 seconds if no outbound traffic has been sent.
This minimal heartbeat ensures that carrier NAT translation tables remain active, guaranteeing that return packets can reach the mobile device without interruption.
RiceGuard Architecture: Zero-Latency Cellular and Wi-Fi Transitions
At VPNRice, mobile tunnel resilience is engineered directly into the core network architecture through the RiceGuard protocol engine. RiceGuard builds upon WireGuard kernel primitives to deliver uncompromised session continuity for roaming users.
[VPNRice RiceGuard Mobile Roaming Ecosystem]
Mobile Smartphone
  [RiceGuard Link Sensor] <---> Detects Wi-Fi / 5G Radio Signal Transitions
          |
          +---> Emits Immediate Authenticated Keepalive on Radio Switch
                     |
                     v (UDP Port Hopping / Wire Image Normalization)
VPNRice Anycast Gateway Core
  [Kernel Roaming Engine] <---> Validates ChaCha20-Poly1305 in Microseconds
          |
          +---> Instantaneous Endpoint Rebinding (0ms Renegotiation Latency)
          +---> Zero Voice Call Dropping / Uninterrupted Streaming
When a smartphone running VPNRice transitions from home broadband Wi-Fi to a 5G mobile cell tower:
- The RiceGuard link-sensing daemon detects interface status changes at the operating system level.
- Rather than waiting for a transmission stall, RiceGuard dispatches an authenticated probe datagram over the newly active cellular interface.
- The receiving VPNRice Anycast edge cluster verifies the cryptographic signature in microseconds, updates its routing table atomically, and diverts all subsequent downstream traffic to the new 5G IP address.
- Active video streams, VoIP calls, and latency-sensitive terminal connections continue seamlessly without freezing, reconnection prompts, or packet loss.
Secure, continuous connectivity on mobile devices requires an architecture built for dynamic environments. By replacing fragile state machines with cryptographically authenticated endpoint roaming, modern VPN networks provide effortless mobility across any physical connection.
Protect your mobile connectivity across every network transition. Get VPNRice.