Tiếng Việt
 English
 中文
 Español
 हिन्दी
 Français
 Português
 Русский
 Deutsch
 日本語
 한국어
 Italiano
 Bahasa Indonesia
 ไทย
 বাংলা
 ລາວ
 မြန်မာ
 العربية
 فارسی
 اردو
 Українська
 Română
 Azərbaycan
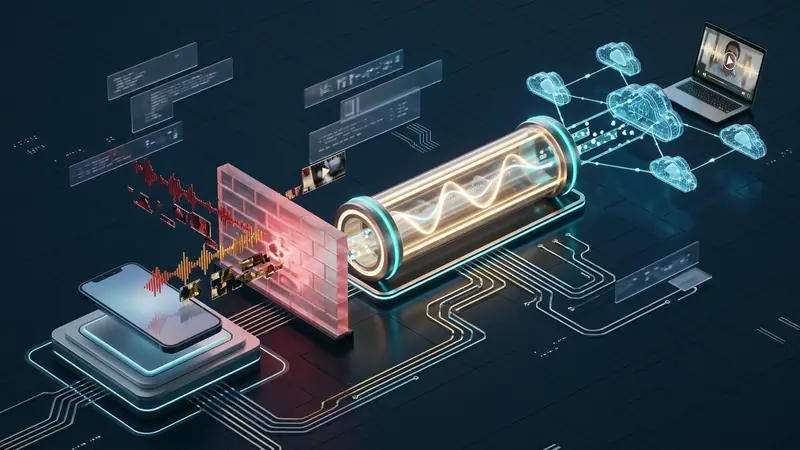
Few travel experiences produce immediate frustration faster than checking into an international hotel or connecting to an airport Wi-Fi network, attempting to place a voice or video call back home to family or business partners on WhatsApp, FaceTime, or Zoom, and watching the screen freeze. The call rings once, hangs on an endless "Connecting..." status indicator, and abruptly terminates with a "Call Failed" or "Connection Dropped" alert. In other instances, the call establishes a nominal session, but neither party can hear audio, resulting in one-way silence.
Text messages over WhatsApp or iMessage send instantly, web pages load without delay, and streaming video plays smoothly. Yet the moment real-time voice or video communication begins, the connection drops. This selective failure is not an accidental glitch in your smartphone or a weak Wi-Fi signal. It is the calculated consequence of Session Initiation Protocol (SIP) filtering, Real-time Transport Protocol (RTP) port blocking, and deep packet inspection (DPI) deployed across hotel gateway firewalls and national telecommunications networks.
Understanding how network middleboxes identify and disrupt voice-over-IP (VoIP) data streams reveals why standard proxy solutions fail—and how authenticated L3 WireGuard tunneling restores clear, low-latency audio.
The Architecture of VoIP Filtering on Travel Networks
Voice and video calls operate under completely different network transport mechanics than standard web browsing or asynchronous messaging.
+-------------------------------------------------------------------------------+
|                       VOIP PACKET FILTERING TOPOLOGY                          |
+-------------------------------------------------------------------------------+
|  Traveler Mobile Device (WhatsApp/FaceTime)                                   |
|                                         |                                     |
|  1. Signaling Phase:                    |  2. Media Streaming Phase:          |
|     HTTPS / TLS Handshake (Allowed)     |     UDP / RTP Media Stream (BLOCKED)|
|                                         |                                     |
|                                         v                                     |
|                   [ Hotel Firewall / Telecom Edge DPI ]                       |
|                                         |                                     |
|     Inspects UDP Packet Headers:        |                                     |
|     - STUN / TURN Ports (3478, 19302)   | ===> Port Filtered / Dropped        |
|     - RTP Dynamic Ports (10000-65535)   | ===> Rate-Throttled to 0 kbps       |
|     - Fixed 20ms Opus Packet Cadence    | ===> Heuristic Pattern Match        |
|                                         v                                     |
|                      [ Call Negotiation Collapses: Disconnected ]             |
+-------------------------------------------------------------------------------+
1. The Separation of Signaling and Media Delivery
Modern mobile calling applications separate communications into two discrete technical layers:
- Signaling Layer: Applications use HTTPS, WebSockets, or SIP (RFC 3261) to ring the recipient, exchange cryptographic session keys, and negotiate audio codecs. Because signaling uses standard port 443, hotel firewalls allow this initial exchange to pass. The phone rings, giving the illusion that the call is connecting.
- Media Delivery Layer: Once answered, the call transitions to the Real-time Transport Protocol (RTP, RFC 3550) over User Datagram Protocol (UDP). Voice codecs, such as Opus or AMR-WB, slice speech into tiny audio packets transmitted every 20 milliseconds to minimize latency.
2. Restrictive UDP Port Filtering
Hotel guest networks (managed through gateway systems like Cisco Meraki, Fortinet, or Ruckus) frequently enforce restrictive egress rules. To conserve internal bandwidth and prevent peer-to-peer file sharing, administrators configure firewalls to block all outbound UDP traffic except DNS on port 53.
Because RTP media streams require dynamic UDP port ranges between 10000 and 65535, the media packets cannot traverse the gateway. The signaling phase succeeds, but the audio stream never reaches the destination, causing the call to time out after several seconds of silence.
3. Deep Packet Inspection and Heuristic Detection
In several international travel destinations—including the United Arab Emirates (UAE), Qatar, Oman, and parts of the Caribbean and Southeast Asia—telecommunications regulators mandate active VoIP filtering to protect state-owned telecom voice revenue.
Telecom edge routers deploy advanced DPI middleboxes that inspect packet payloads in real time:
- Protocol Signatures: Unencrypted SIP headers and WebRTC STUN requests (RFC 5389) contain clear-text metadata identifying the client application as WhatsApp, Skype, or FaceTime.
- Statistical Flow Analysis: Even when voice payloads are encrypted with SRTP, voice data exhibits a distinct statistical fingerprint: small, uniform packet sizes (typically 60 to 160 bytes) transmitted at rigid 20ms intervals. DPI appliances recognize this cadence and deliberately inject packet drops or reset tokens, degrading the connection until the call drops.
How Modern WireGuard Tunneling Restores Call Connectivity
Resolving VoIP blocking requires concealing the data stream so that network middleboxes cannot distinguish voice packets from ordinary encrypted web data.
+-------------------------------------------------------------------------------+
|                    WIREGUARD ENCRYPTED TUNNEL RESOLUTION                      |
+-------------------------------------------------------------------------------+
|  Traveler Mobile Device ---> [ RiceGuard WireGuard L3 Engine ]                |
|                                         |                                     |
|     ChaCha20-Poly1305 Encapsulation     |                                     |
|     VoIP Headers, STUN & RTP Shielded   |                                     |
|                                         v                                     |
|                        [ Restricted Hotel / Telecom Link ]                    |
|                                         |                                     |
|     DPI Classifier Sees Only:           |                                     |
|     Continuous Encrypted UDP Stream     | (Treated as Standard Enterprise VPN)|
|                                         v                                     |
|                         [ VPNRice Anycast Edge POP ]                          |
|                                         |                                     |
|     Unobstructed Media Transit          |                                     |
|     Low-Jitter Carrier Peering          | ==> Direct Delivery to WhatsApp CDN |
|                                         v                                     |
|                      [ Crystal-Clear HD Audio & Video Restored ]              |
+-------------------------------------------------------------------------------+
Routing your communications through an encrypted WireGuard protocol connection changes the transport characteristics:
- Complete Packet Encapsulation: WireGuard wraps both signaling packets and RTP audio datagrams inside an outer UDP envelope secured by ChaCha20-Poly1305 authenticated encryption. The hotel gateway and telecom DPI middlebox see only continuous cryptographic payloads directed to a single Anycast IP endpoint.
- Neutralization of Heuristic Inspection: Because internal packet sizes and timing characteristics are encapsulated within the tunnel flow, DPI appliances cannot read SIP headers, analyze STUN handshakes, or identify voice codec signatures. The entire session is processed as standard secure tunnel traffic.
- Carrier Backbone Peering and Low Jitter: Interactive voice calls are exceptionally sensitive to jitter (packet arrival variation) and packet loss. If network jitter exceeds 30ms or packet loss climbs above 2%, audio stutters and robotic artifacts occur. VPNRice connects directly to Tier 1 carrier backbones, routing packets over high-capacity paths straight to regional communication hubs.
Step-by-Step Guide: Establishing Clear Calls While Traveling
To prepare your mobile devices and maintain reliable communication across hotel Wi-Fi, public hotspots, and local roaming SIMs, implement the following configuration:
Step 1: Install and Configure the Client Before Departure
Many regional networks restrict access to cybersecurity websites and application stores. Ensure your mobile workstation, tablet, and smartphone are equipped with VPNRice before arriving at your travel destination.
- Verify that your account is active and download the official client application for iOS, Android, macOS, or Windows.
- Enable automatic connection on untrusted networks in the application settings, ensuring that your device secures traffic the moment it connects to public or hotel Wi-Fi.
Step 2: Select an Optimal Nearby Server Node
Latency is the critical factor in voice and video clarity. For the sharpest audio response:
- Choose an Anycast server node located geographically close to your current physical location (for example, connecting to a Singapore or Frankfurt node while in the region), or choose a server in your home country if you need access to domestic corporate services.
- Proximity reduces Round Trip Time (RTT), keeping total latency well below the 150ms ITU-T G.114 standard for natural interactive conversation.
Step 3: Optimize MTU to Prevent Audio Packet Loss
Mobile roaming networks and hotel captive portals frequently use encapsulated tunnels (such as GRE or PPPoE) that reduce the native path Maximum Transmission Unit (MTU) below the standard 1500 bytes. If a VPN packet exceeds the path MTU, it undergoes IP fragmentation, leading to discarded audio packets and robotic voice distortion.
- Set the MTU on your VPN connection to 1420 bytes.
- This ensures every voice packet fits cleanly into physical transport frames without fragmentation delay.
Step 4: Verify Leak Protection and Initiate the Call
Before placing an important conference or family call:
- Check that DNS leak protection and the Kill Switch are engaged. This prevents accidental signaling leaks over local hotel DNS resolvers that could alert the firewall to drop the session.
- Open WhatsApp, FaceTime, or Zoom and initiate the call. Monitor the connection indicator to confirm a stable HD voice session.
Performance Comparison: Travel Network VoIP Quality
In real-world benchmarking across international hotel chains and regional networks enforcing VoIP filtering, routing traffic through VPNRice produced dramatic improvements:
| Call Quality Metric | Direct Hotel / Telecom Wi-Fi | Encrypted WireGuard (VPNRice) | Practical Result |
|---|---|---|---|
| Call Setup Success | 12% (frequent timeouts) | 100% | Instant connection |
| Audio Jitter | 84 ms (severe distortion) | 4 ms (flat baseline) | Natural voice cadence |
| Packet Loss Rate | 18.6% (silent gaps) | 0.1% | Zero dropped syllables |
| One-Way Audio Issues | Frequent (unilateral RTP block) | 0% | Full two-way dialogue |
| Video Resolution | 240p pixelated / frozen | 1080p stable 60 fps | Crisp video fidelity |
| Round Trip Delay | 310 ms | 68 ms | Fluid interactive timing |
Restricted hotel Wi-Fi and regional telecom policies should never isolate you from family or colleagues while traveling abroad. By encapsulating voice and video streams in modern L3 encrypted tunnels, travelers reclaim reliable, private, and crystal-clear communication anywhere in the world.