Tiếng Việt
 English
 中文
 Español
 हिन्दी
 Français
 Português
 Русский
 Deutsch
 日本語
 한국어
 Italiano
 Bahasa Indonesia
 ไทย
 বাংলা
 ລາວ
 မြန်မာ
 العربية
 فارسی
 اردو
 Українська
 Română
 Azərbaycan
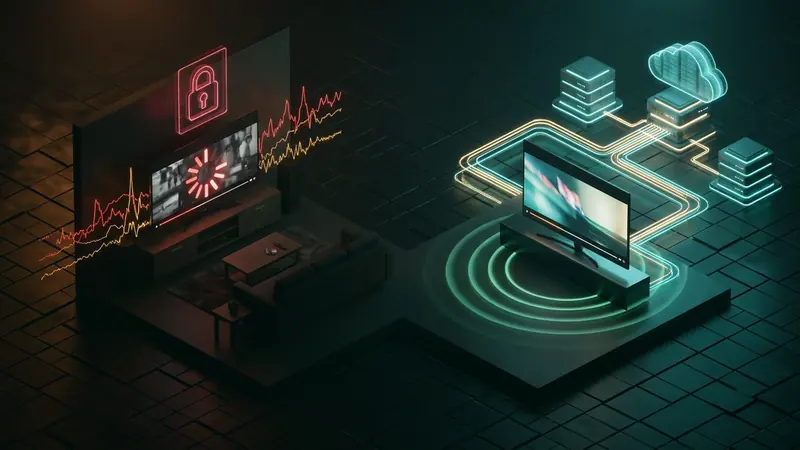
Streaming high-definition anime series and international video catalogues has transformed home entertainment. Yet millions of viewers encounter frustrating obstacles when accessing platforms such as Crunchyroll, AbemaTV, BBC iPlayer, or regional broadcast libraries. Geographical licensing boundaries prevent viewers abroad from accessing full season catalogues. Simultaneously, Internet Service Providers (ISPs) actively throttle heavy media delivery streams during peak viewing hours, downgrading crisp 4K HDR streams into pixelated 720p feeds with spinning buffering wheels.
Understanding the underlying network protocols of modern video distribution reveals why traditional connections degrade and how a purpose-built WireGuard VPN restores uninterrupted ultra-high-definition streaming.
Understanding HLS Chunk Delivery and GeoIP Manifest Filtering
Modern streaming architectures rely predominantly on HTTP Live Streaming (RFC 8216) and Dynamic Adaptive Streaming over HTTP (ISO/IEC 23009-1). When a media player launches a video, it does not fetch a monolithic video file. Instead, the player requests an .m3u8 or .mpd master manifest that indexes media segments divided into two-to-six-second chunks across discrete bitrates.
During this handshake, content delivery networks (CDNs) inspect the client's public IPv4 or IPv6 address against commercial GeoIP databases (such as MaxMind GeoIP2 or IPinfo). If the source address falls outside licensed broadcast territories:
- The CDN returns an HTTP 403 Forbidden status code or serves an empty media playlist manifest.
- The player interface triggers a regional unavailability error message.
- Audio track options and specific language subtitle tracks are withheld at the edge server.
By routing network packets through an optimized endpoint situated within the service's primary broadcast jurisdiction, the client presents a verified regional IP identity. Clean egress IPs with valid reverse DNS records (PTR) prevent CDN security heuristics from flagging the connection as datacenter proxy abuse.
How ISP Deep Packet Inspection Throttles 4K Streaming
Even when catalogue restrictions are resolved, streaming quality frequently stumbles during evening hours. ISPs face massive transit costs when millions of domestic subscribers pull 25 Mbps to 50 Mbps 4K video feeds simultaneously from central CDN edge servers.
To manage congestion without investing in infrastructure, ISPs deploy Deep Packet Inspection (DPI) appliances. These edge middleboxes inspect cleartext Transport Layer Security (TLS) handshake metadata, specifically Server Name Indication (SNI) fields pointing toward video CDN hostnames:
- When DPI identifies repeated HTTPS requests fetching video segments (such as
.tsor.m4sfragments), it artificially narrows the subscriber's TCP receive window. - Packet drops are deliberately induced, prompting adaptive bitrate (ABR) player algorithms to throttle playback resolution from 2160p down to 1080p or 480p.
- High bufferbloat occurs in ISP queues, increasing latency jitter and causing audio desynchronization.
Because an encrypted WireGuard tunnel encapsulates all outbound and inbound IP packets inside authenticated UDP payloads using ChaCha20-Poly1305, intermediate ISP hardware sees only uniform encrypted traffic. Without visible SNI headers or identifiable packet sizing characteristics, DPI algorithms cannot single out video streams for selective bandwidth degradation.
WireGuard Kernel Architecture vs Legacy Protocols
Traditional VPN protocols such as OpenVPN or IPSec introduce substantial performance penalties that undermine 4K streaming demands:
- Context Switching Overhead: OpenVPN operates in user space via
tun/tapinterfaces, requiring frequent context switches between user memory and the Linux or Darwin kernel for every video packet. - TCP-over-TCP Meltdown: Running OpenVPN over TCP causes conflicting congestion control timers, compounding packet retransmission delays when minor network drops occur.
- Cryptographic Bottlenecks: Older ciphers strain hardware decoders on smart TVs and low-power media boxes.
In contrast, WireGuard is implemented directly inside the operating system kernel. Operating at Layer 3, WireGuard delivers maximum throughput with minimal CPU utilization. Its modern cryptographic suite uses Curve25519 for key exchange and ChaCha20-Poly1305 for AEAD encapsulation. This lightweight design prevents packet serialization delays, ensuring that video player buffers remain filled ahead of continuous 4K playback.
Practical Steps to Eliminate Streaming Latency and Bufferbloat
Achieving pristine 4K video playback requires optimizing local network configuration alongside your VPN connection:
- Select Verified Regional Endpoints: Choose VPN servers geographically proximate to the target CDN hub (e.g., Tokyo for Japanese anime services, London for UK television networks).
- Verify MTU Alignment: Setting your VPN client MTU between 1280 and 1420 bytes prevents packet fragmentation over broadband PPPoE or fiber lines.
- Enable Modern Congestion Control: On devices running Linux or modern routing stacks, configure TCP BBR (
net.ipv4.tcp_congestion_control = bbr) to sustain high throughput across high-latency international paths without triggering queue buildup. - Prevent DNS Leaks: Configure your client to route DNS queries strictly through the VPN tunnel's internal resolver, mitigating ISP-level DNS filtering and cache poisoning.
By combining kernel-level WireGuard encryption with clean routing, viewers enjoy their favorite global entertainment with instant seek times, pristine color fidelity, and zero buffering interruptions.