Tiếng Việt
 English
 中文
 Español
 हिन्दी
 Français
 Português
 Русский
 Deutsch
 日本語
 한국어
 Italiano
 Bahasa Indonesia
 ไทย
 বাংলা
 ລາວ
 မြန်မာ
 العربية
 فارسی
 اردو
 Українська
 Română
 Azərbaycan
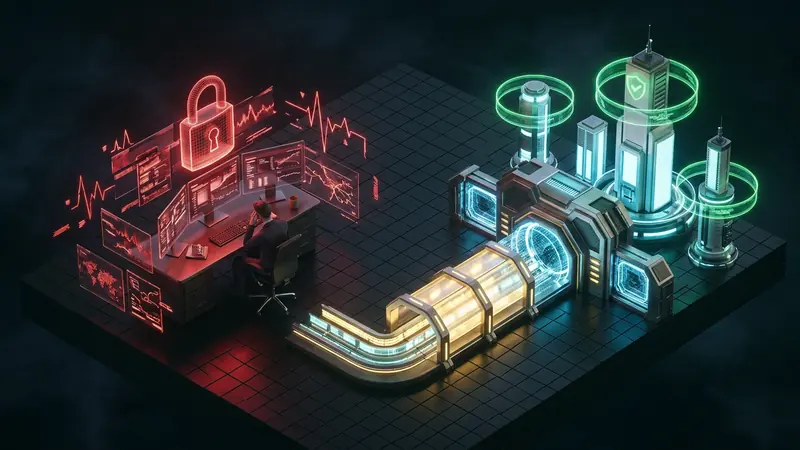
Operating an online store on global marketplaces such as Amazon, eBay, Etsy, or Shopify across international borders is a core business model for independent entrepreneurs. Yet thousands of cross-border sellers face sudden account checkpoints, forced re-verifications, or catastrophic permanent suspensions every month. Most sellers assume their supplier documents or listing descriptions triggered the compliance department. In reality, modern marketplace risk engines evaluate underlying network telemetry before examining commercial listings.
Understanding the technical mechanics behind automated merchant fraud scoring reveals why consumer network habits trigger automated account freezes, and how establishing a disciplined, cryptographic networking pipeline keeps international storefronts operational.
Anatomy of Marketplace Risk Scoring and IP Velocity
Modern e-commerce platforms run automated anti-fraud engines such as Sift Science, Riskified, and proprietary machine-learning heuristics. These algorithms monitor account sessions in real time, assigning a cumulative fraud score based on network anomalies:
- IP Velocity Scoring: If an account signs in from Hanoi at 09:00 UTC and submits inventory modifications from Frankfurt at 09:45 UTC, the physical transit time between geographical coordinates violates physics. Automated risk engines flag this impossible travel speed as credential stuffing or account takeover.
- Autonomous System Number (ASN) Classification: Risk engines cross-reference incoming client IP addresses against global threat intelligence databases (MaxMind GeoIP2 Anonymous IP, Spamhaus, IPQualityScore). Commercial cloud hosting ASNs (such as Amazon AWS, DigitalOcean, or Hetzner) carry high fraud coefficients because fraudsters routinely spin up cheap virtual private servers for automated scraping and fraudulent storefront deployment.
- Subnet Reputation and Contamination: When multiple merchants share cheap consumer VPN endpoints, malicious activity from one bad actor taints the entire
/24subnet. If another account on that subnet commits payment chargebacks or policy violations, automated anti-syndicate rules freeze every associated account on that IP block.
| Telemetry Vector | Clean Residential / Dedicated Egress | Cheap Datacenter Proxy |
|---|---|---|
| ASN Classification | ISP / Commercial Broadband | Hosting / Datacenter (Flagged) |
| Fraud Risk Score | Minimal (< 10/100) | Critical (> 80/100) |
| Subnet Sharing | Dedicated or Controlled Range | Thousands of Rotating Users |
| WebRTC Exposure | Shielded via In-Kernel Tunnel | Exposed Real Public IP |
Browser Fingerprinting and the Multi-Store Association Trap
Cross-border sellers frequently operate separate brand storefronts to target distinct consumer niches or mitigate product risks. Marketplace operating policies strictly prohibit unapproved multiple accounts, employing automated link-analysis graphs to detect unauthorized multi-store operations.
Risk engines do not merely read HTTP cookies; they construct persistent device fingerprints via Canvas rendering tests, WebGL shader execution profiling, AudioContext frequency analysis, and battery API state. When a seller switches browser profiles on the same computer without isolated network routing, platform telemetry correlates the connections instantly.
+-----------------------------------------------------------+
|             Seller Workstation Architecture               |
|                                                           |
|  [Storefront A - US Market]    [Storefront B - EU Market] |
|              |                             |              |
|     (Clean Profile A)             (Clean Profile B)       |
|              \                           //              |
|        Isolated Route A            Isolated Route B       |
|              v                             v              |
|     [WireGuard US Gateway]       [WireGuard EU Gateway]   |
|        (Static Egress)              (Static Egress)       |
|              |                             |              |
|              v                             v              |
|     [Amazon US Portal]           [Amazon EU Portal]       |
+-----------------------------------------------------------+
Even with dedicated browser profiles, an unshielded network link exposes local WebRTC candidates through Interactive Connectivity Establishment (ICE) requests. When your browser queries STUN/TURN servers to initialize media capabilities, it broadcasts your true ISP assigned public IP address in parallel with proxy traffic. The marketplace server logs the WebRTC candidate, links both store accounts to your domestic connection, and triggers an automated chain suspension.
How In-Kernel WireGuard Protects Storefront Operations
Resolving network-level account suspensions requires replacing unstable proxy extensions with kernel-level packet encapsulation. WireGuard operates directly within the operating system kernel (Layer 3), establishing an encrypted network interface that treats all business traffic symmetrically.
Deterministic Routing and Split-Tunneling
Operating an international store while conducting local communication creates operational friction if all computer traffic travels overseas. Split-tunneling allows merchants to route administrative marketplace dashboards, payment processor portals (PayPal, Stripe), and inventory APIs through dedicated encrypted endpoints, while local messaging apps, banking apps, and domestic streaming continue through the primary ISP connection.
This separation prevents accidental IP contamination. Local browsing habits never interact with marketplace security cookies, and administrative sessions maintain an unvarying, predictable egress footprint.
Cryptographic Identity and Zero Packet Leakage
WireGuard utilizes Noise Protocol handshakes with Curve25519 elliptic-curve key exchange, ChaCha20 encryption, and Poly1305 authentication. Because the handshake is stateless and authenticated cryptographically, temporary connection drops do not expose plaintext DNS queries or raw TCP handshakes to local networks. A dedicated kill-switch halts outbound application traffic instantly if the tunnel reconnects, guaranteeing that marketplace sessions never transmit an unencrypted packet from an unexpected geographical location.
Recommended Network Hygiene for International Merchants
Maintaining long-term account health requires systematic network discipline alongside clean software tools:
- Assign Dedicated Egress Points per Store: Never access Storefront A and Storefront B from the same network endpoint within identical working sessions. Maintain dedicated static IP gateways for each regional brand.
- Enforce Strict WebRTC Mitigation: Configure browser instances to disable non-proxied UDP traffic via administrative policies, ensuring that WebRTC requests never transmit STUN packets outside the active WireGuard interface.
- Eliminate Mobile Hotspot Switching: Avoid managing critical account listings while tethered to unstable mobile cellular connections. Cellular NAT gateways frequently reassign IP addresses across disparate geographic ranges, generating false IP velocity flags.
- Audit Subnet Cleanliness Periodically: Query trusted threat databases to verify that your active egress IP maintains a low fraud rating and contains no active spam or malicious activity listings.
By establishing disciplined, kernel-level encrypted routing with clean static egress addresses, cross-border merchants shield their operational infrastructure against automated risk engine penalties and secure uninterrupted access to global markets.